Question 1
What causes authentication failures on a Cisco WSA when LDAP is used for authentication?
Answer and explanation
Correct answer: B

17 free sample questions232 in the full practice test
What causes authentication failures on a Cisco WSA when LDAP is used for authentication?
Correct answer: B
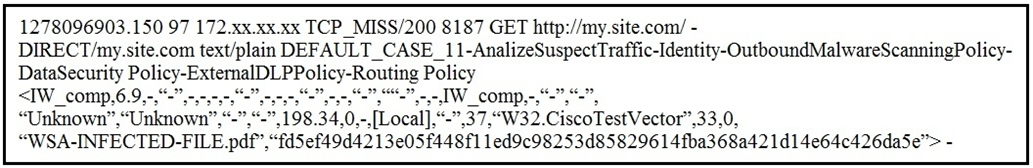
Refer to the exhibit. Which statement about the transaction log is true?
Correct answer: D
Which two features can be used with an upstream and downstream Cisco WSA web proxy to have the upstream WSA identify users by their client IP address?(Choose two.)
Correct answers: A, D
Which two configuration options are available on a Cisco WSA within a decryption policy? (Choose two.) A.Pass ThroughB.WarnC.DecryptD.AllowE.Block
Correct answers: A, C
An administrator is configuring WCCP to redirect traffic from a Cisco Catalyst switch to a Cisco Web Security Appliance (WSA). The deployment requires the WSA to return traffic to the switch using a different interface than the one used for ingress traffic to avoid routing loops. Which WCCP forwarding method must be configured on both devices to support this topology?
Correct answer: B
GRE encapsulation allows the WSA to be located on a different subnet or interface than the clients/routers and supports returning traffic via specific interfaces. L2 redirection requires Layer 2 adjacency.
A security architect is designing a transparent proxy deployment for a branch office. The requirement is to preserve the original client IP address in the logs of the upstream web servers for auditing purposes. Which feature should be enabled on the Cisco WSA?
Correct answer: A
In transparent mode, enabling IP Spoofing allows the WSA to use the client's IP address as the source IP when connecting to the destination server, preserving it for server-side logging.
While troubleshooting an authentication issue, an administrator observes that users are being repeatedly prompted for credentials when accessing the internet. The WSA is configured for NTLM authentication. Which of the following conditions is the most likely cause of this behavior?
Correct answer: A
Kerberos and NTLM (depending on security settings) are sensitive to time synchronization. If the WSA clock skews significantly (usually > 5 mins) from the DC, authentication tokens are rejected, causing repeated prompts.
A multinational corporation uses a PAC file to direct user traffic. They want to ensure that if the primary WSA (10.1.1.10) is unavailable, traffic automatically fails over to the secondary WSA (10.1.1.20), and if both fail, traffic goes DIRECT. Which JavaScript return statement correctly implements this logic?
Correct answer: A
PAC files process return values in order. The browser tries the first proxy; if it fails/times out, it tries the second, and finally falls back to DIRECT.
Register free to unlock 9 more sample questions
Own this practice test forever.
Any 2 exams per month.
Any 4 exams per month.
Any 12 exams over 3 months.


