Covers business risk mitigation, integrating network, host and mobile security controls, security assessments and incident response, cloud and authentication integration, and industry research trends.
17 free sample questions361 in the full practice test Other versions: CAS-005(210),CA1-005(215),CAS-004(149)
A company’s Chief Operating Officer (COO) is concerned about the potential for competitors to infer proprietary information gathered from employees’ social media accounts. Which of the following methods should the company use to gauge its own social media threat level without targeting individual employees?
Answer and explanation
Correct answer: A
A
Q2Question 2
Multiple answers
A security administrator is hardening a TrustedSolaris server that processes sensitive data. The data owner has established the following security requirements:
The data is for internal consumption only and shall not be distributed to outside individuals The systems administrator should not have access to the data processed by the server The integrity of the kernel image is maintained
Which of the following host-based security controls BEST enforce the data owner’s requirements? (Choose three.)
Answer and explanation
Correct answers: C, E, F
C, E, F
Q3Question 3
Multiple answers
An SQL database is no longer accessible online due to a recent security breach. An investigation reveals that unauthorized access to the database was possible due to an SQL injection vulnerability. To prevent this type of breach in the future, which of the following security controls should be put in place before bringing the database back online? (Choose two.)
Answer and explanation
Correct answers: C, F
C, F
Q4Question 4
A company has entered into a business agreement with a business partner for managed human resources services. The Chief Information Security Officer (CISO) has been asked to provide documentation that is required to set up a business-to-business VPN between the two organizations.
Which of the following is required in this scenario?
Answer and explanation
Correct answer: A
A
Q5Question 5
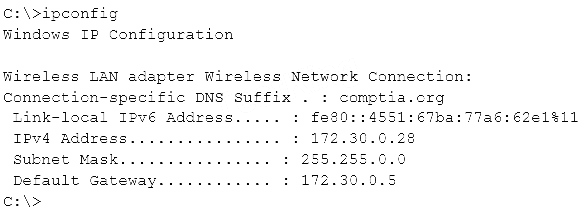
Given the output blow from a local PC.
Which of the following ACLs on a stateful host-based firewall would allow the PC to serve an intranet website?
Answer and explanation
Correct answer: B
B
Q6Question 6
A penetration tester has been contracted to conduct a physical assessment of a site. Which of the following is the MOST plausible method of social engineering to be conducted during this engagement?
Answer and explanation
Correct answer: B
B
Q7Question 7
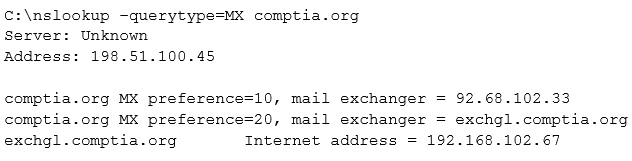
A penetration tester is conducting an assessment on Comptia.org and runs the command below from a coffee shop while connected to the public Internet.
Which of the following should the penetration tester conclude about the command output?
Answer and explanation
Correct answer: B
B
Q8Question 8
Two new technical SMB security settings have been enforced and have also become policies that increase secure communications.
Network Client: Digitally sign communication
Network Server: Digitally sign communication
A storage administrator in a remote location with a legacy storage array, which contains timesensitive data, reports employees can no longer connect to their department shares. Which of the following mitigation strategies should an information security manager recommend to the data owner?
Answer and explanation
Correct answer: A
A
Register free for 9 more questions
Or unlock all 361 CAS-003 questions with explanations, timed mode and flashcards.