
SC-401 Exam 2026 Changes: Sentinel KQL and Threat Hunting Replace Log Analytics
If you have been preparing for the SC-401 exam using materials from late 2025, your study plan needs a hard reset. Microsoft has shifted the skills measured on this test away from legacy log-analytics scenarios and toward hands-on Sentinel KQL queries and threat-hunting tasks. The change is not cosmetic. Candidates who walk in expecting to click through Azure Monitor workbook questions are now facing interactive labs that ask them to write KQL to detect lateral movement, correlate alerts across Entra ID and Defender, and build hunting queries from raw telemetry.
This update matters because the SC-401 only went live in early 2025 as the replacement for the retired SC-400. Many training providers and self-study guides were still catching up to the original blueprint when Microsoft began rolling in these practical security operations tasks. The result is a gap between what a lot of practice materials cover and what the live exam actually asks.
Here is what changed, when it took effect, and how to find SC-401 sample questions that reflect the current test.
What Microsoft Changed and When
The SC-401: Administering Information Security in Microsoft 365 exam was refreshed in two waves during 2026. The first wave, documented in April, brought minor grammatical and wording updates to the official study guide but left the topic list intact. The second wave, announced for August 2026, is the substantial one: it retires the learning path "Protect data in AI environments with Microsoft Purview" and replaces it with "Secure AI interactions and environments with Microsoft Purview," structured around five job-task modules rather than product features.
More importantly for security operations candidates, the live exam has begun emphasizing Sentinel KQL and threat hunting in place of the older log-analytics-centric scenarios. This aligns with broader industry pressure to make certifications test what administrators actually do day-to-day. According to Microsoft guidance, the refreshed content "better match[es] how people actually work with AI security—focusing more on real-world tasks than just product features."
The official skills guide, last updated 31 May 2026, still lists three domains weighted 30–35% each:
- Implement information protection
- Implement data loss prevention and retention
- Implement information security, compliance, and AI governance
Within that third domain, the practical application of Sentinel for threat detection has moved from peripheral to central. Where older versions of the exam might have asked you to interpret a pre-built workbook, the current version expects you to construct or complete KQL queries that hunt for specific attack patterns.
From Log Analytics to Sentinel KQL: What the Shift Looks Like
Legacy SC-401 preparation often treated Azure Log Analytics as the primary telemetry workspace. You learned to write basic queries to filter sign-in logs, chart failed authentication attempts, and set alert thresholds. That knowledge is not wasted—Log Analytics remains the underlying data engine—but the exam now frames those tasks inside Microsoft Sentinel.
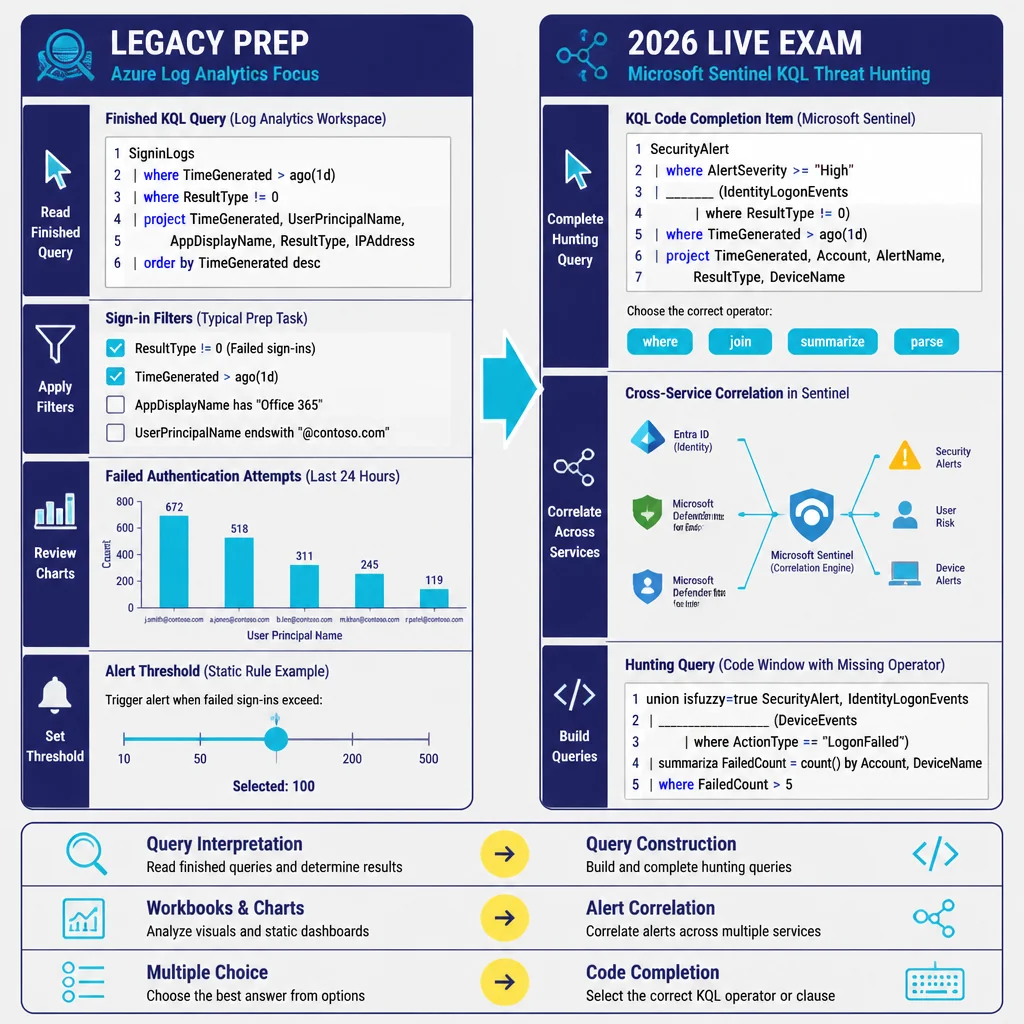
This means three concrete differences in question style:
Query construction over query interpretation. Instead of reading a finished query and identifying what it does, you may need to select the correct KQL operator to complete a hunting query. Expect to see incomplete union, join, parse, or extend statements where you supply the missing clause to correlate SecurityAlert and IdentityLogonEvents tables.
Cross-service correlation. The new scenarios force you to connect Sentinel with Microsoft Defender for Endpoint, Defender for Identity, and Entra ID Protection. A single question might present a simulated incident timeline and ask you to write KQL that pulls device risk, user risk, and email anomaly data into one result set.
Threat-hunting methodology. Beyond syntax, questions now test process. You might be asked which hunting hypothesis to pursue first given a set of anomalous indicators, or which KQL pattern best supports a specific MITRE ATT&CK technique mapping.
This is a significant jump in technical depth from the earlier SC-400 and first-release SC-401. As one independent guide noted, candidates who "show up with old SC-400 study materials and assume they'll coast are the ones posting about their 650 scores."
How the Exam Format Handles Practical Skills
The SC-401 exam itself runs 100 minutes with roughly 40–60 items, including multiple-choice, drag-and-drop, matching, and case-study formats. The practical KQL and threat-hunting content does not appear as a separate lab section. Instead, it is woven throughout the third domain as interactive item types.
You might encounter:
- Code completion: A partial KQL query with four possible
whereclause options. Only one filters the SecurityEvent table to surface credential dumping attempts without excluding legitimate service account activity. - Sequence ordering: Drag query-building steps into the correct order for a hunting workflow—hypothesis formation, data source selection, initial KQL pivot, enrichment join, and IOC export.
- Case-study integration: A multi-question scenario built around a simulated breach where your KQL choices in question three determine what data is available for question four.
The case-study format is particularly unforgiving if your KQL fundamentals are weak. Wrong early choices lock you into incomplete data sets for later questions, just as they would in a real SOC investigation.
Why Microsoft Moved Away from Pure Purview Administration
The SC-401 was never meant to be a Purview-only exam, despite the common nickname. Its full title is "Administering Information Security in Microsoft 365," and Microsoft's security stack has consolidated around Sentinel as the central SIEM and SOAR layer. The exam refresh reflects that architecture.
Several industry trends support this direction. A 2026 CIO analysis found that certification vendors across the board are "reworking testing environments to better reflect the modern world," with hands-on, skills-based criteria replacing memorization-heavy formats. Pearson's 2026 employer research similarly notes that 78% of organizations now choose professional certification as their leading upskilling investment, with preference given to credentials that validate practical capability over theoretical knowledge.
For Microsoft specifically, the Sentinel shift also addresses a persistent criticism: that their security certifications tested product navigation more than security operations thinking. KQL-based threat hunting forces candidates to demonstrate both.
Finding Current SC-401 Sample Questions That Match the Live Exam
This is where many candidates stall. A search for SC-401 sample questions still returns a lot of material built for the original 2025 launch or recycled from SC-400. That content will not prepare you for Sentinel KQL interactions.
Here is how to evaluate whether your practice sources are current:
Check the publication date and changelog. Any material dated before April 2026 should be treated with suspicion. Even April–June 2026 content may only reflect the minor grammatical update, not the August skills refresh.
Look for explicit KQL coverage. Legitimate current practice tests include interactive or text-based KQL questions, not just multiple-choice about Sentinel features. If the table of contents lists "Azure Monitor" but not "Sentinel hunting queries," the material is outdated.
Verify threat-hunting scenarios. Current sample questions should present MITRE-mapped attack chains and ask you to select or build appropriate detection logic. Pure policy-configuration questions dominate older material.
Test the explanations. Quality practice providers explain why a particular KQL operator works, not just which answer is correct. You need to learn the pattern, not memorize the choice.
PlanetCert's Microsoft practice tests are updated to reflect the August 2026 objectives, including Sentinel KQL and cross-service correlation scenarios. The simulator format lets you work through timed, exam-style interactions rather than static PDFs, which matters for building speed with KQL syntax under pressure.
Building a Study Plan Around the New Objectives
With the shift to practical skills, rote memorization of Purview policy settings will not carry you. A focused four-week study plan for the current SC-401 might look like this:
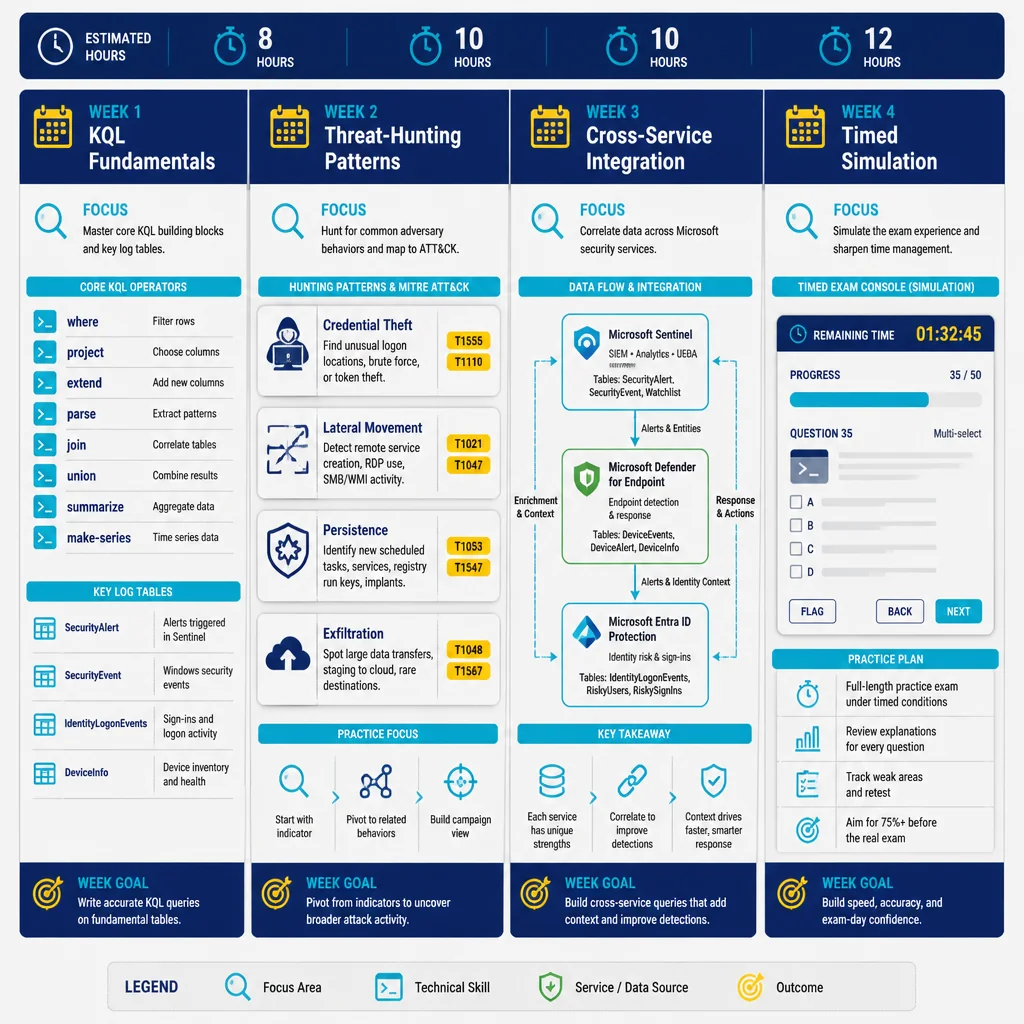
Week 1: KQL fundamentals. Master the core operators—where, project, extend, parse, join, union, summarize, and make-series. Practice against the free Sentinel demo environment or your own tenant's logs. Focus on SecurityAlert, SecurityEvent, IdentityLogonEvents, and DeviceInfo tables.
Week 2: Threat-hunting patterns. Study common detection logic for credential theft, lateral movement, persistence, and exfiltration. Map each to MITRE ATT&CK techniques. Practice writing queries that pivot from an initial indicator to a broader campaign view.
Week 3: Cross-service integration. Build queries that correlate Sentinel with Defender for Endpoint, Entra ID Protection, and Purview DLP alerts. Understand how data flows between these services and where each table's strengths lie.
Week 4: Timed simulation. Run full-length practice exams that include the interactive item types. Review every incorrect KQL answer by rewriting the query yourself in a sandbox until the logic clicks.
This structure front-loads technical skill and reserves the final week for exam mechanics. Candidates who reverse this—spending three weeks on flashcards and one on KQL—often report running out of time during the live test.
What the August 2026 Course Update Adds
Microsoft's official SC-401T00 instructor-led training is being refreshed to match the new learning path. The five modules in "Secure AI interactions and environments with Microsoft Purview" cover:
- Understanding Purview protections for AI
- Securing Microsoft 365 Copilot interactions
- Securing enterprise and non-Microsoft AI applications
- Securing developer AI environments
- Using Data Security Posture Management (DSPM) for AI risk assessment
These modules do not replace Sentinel KQL study. They sit alongside it, testing your ability to apply information security governance to AI-specific risks. Expect exam questions that ask you to choose between DLP policies, sensitivity labels, and Sentinel hunting queries depending on whether a scenario involves regulated data in a Copilot chat, a third-party LLM integration, or a suspected prompt-injection attack.
The DSPM for AI module is especially worth attention. It is new to the Microsoft certification ecosystem and relatively thin in third-party study materials. The official Microsoft guidance covers it at a high level; you will need to supplement with hands-on Purview portal exploration.
Common Preparation Mistakes to Avoid
Three errors show up repeatedly in candidate feedback from failed attempts:
Studying SC-400 material. The overlap is roughly 60% at a topic level but diverges sharply in implementation detail. SC-400's emphasis on Azure Information Protection and classic DLP policies does not cover Sentinel hunting or AI governance.
Ignoring KQL syntax precision. The exam does not require you to be a KQL expert, but small errors—using == instead of =, forgetting tostring() on dynamic fields, or joining on the wrong key—will produce wrong answers in code-completion items.
Neglecting time management. Interactive items take longer than multiple-choice. If you spend four minutes perfecting a hunting query, you may not finish the case study. Practice under timed conditions until you can read, analyze, and answer KQL questions in under two minutes each.
Reader Questions
How do I know if my practice test provider has updated for the August 2026 changes?
Look for a published changelog or version date on the exam page. Current providers explicitly list "Sentinel KQL," "threat hunting," or "August 2026 objectives" in their coverage. If the marketing copy still emphasizes "Purview administration" without mentioning security operations, the content is likely stale.
Is the SC-401 harder than the old SC-400?
The pass rate data is not public, but the skills tested are more applied. SC-400 rewarded product knowledge; SC-401 rewards product knowledge plus query-writing and investigative reasoning. Candidates with SOC experience find the transition natural. Those coming from compliance or governance backgrounds often need extra KQL preparation.
Does the exam include actual hands-on labs or just simulated questions?
The live exam uses interactive item types within a standard test interface, not a full virtual lab. You will select, order, or complete KQL statements rather than typing freely into a query editor. However, the cognitive load is similar—you must understand what the query does, not just recognize keywords.
Will Microsoft update the exam again soon?
Microsoft typically refreshes role-based exams annually and retires them after roughly two years. Given that SC-401 launched in early 2025 and received this substantial update in 2026, another refresh is likely in 2027. Plan to sit the exam within six months of preparation to avoid further drift.
What to Watch Next
Two developments could affect SC-401 candidates in late 2026 and early 2027:
First, Microsoft may extend the AI governance content further as Copilot and third-party LLM integrations mature. The DSPM for AI module is a foundation; expect deeper coverage of prompt-injection detection, model risk scoring, and automated remediation workflows.
Second, the broader certification industry is pushing toward even more practical assessment formats. Pearson's 2026 research notes employer demand for "validated skills" over "credential accumulation." Microsoft could introduce performance-based testing elements—actual query execution against a sandbox—into future security exams.
For now, the priority is clear: master Sentinel KQL, practice threat-hunting methodology, and verify that every sample question you study reflects the August 2026 objectives.
References
Sc 401 Administering Information Security — SC-401: Administering Information Security in Microsoft 365 Exam Resource Guide (April 2026 Update) – intunedin.net ... SC-401 received its first update since it became generally
Discussion
Question Comments
0 comments·0 participantsSign in to leave a comment and access more free questions.