
Cisco Certified Network Associate (CCNA) Free Sample Questions

Create a free account to browse all 23 sample questions. The full practice test includes 548 questions. Use the simulator for timed and flashcard mode. Or, view more alternate versions 200-105 257 Questions 200-125 70 Questions.

Try Simulator

200-301 Sample Questions

  1. Question 1

    Q1

    You are the network administrator for your company and have configured Cisco Discovery Protocol (CDP) in your network. You recently noticed that when devices send large numbers of CDP neighbor announcements, some devices are crashing. You decide to disable CDP on the router.

    Which command should you use to achieve the objective?

    Show answer & explanation

    Correct answer: A

    The no cdp run command globally disables Cisco Discovery Protocol (CDP) on the entire router, providing complete protection against CDP-based denial-of-service attacks and information disclosure vulnerabilities. CDP operates at Layer 2 and broadcasts detailed device information including IOS version, platform type, and capabilities, which can be exploited by attackers. The other options use invalid commands - set cdp disable is not valid Cisco IOS syntax, no cdp enable attempts to disable a non-existent enable command, and no cdp advertise-v2 only disables CDP version 2 advertisements while leaving the protocol vulnerable. Complete CDP disabling with no cdp run is the recommended security practice in environments where device discovery is not required.
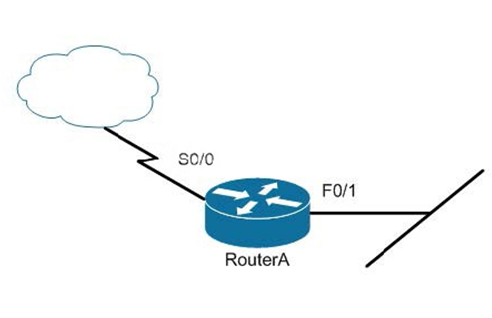
  2. Question 2

    Q2

    Which is NOT a valid range for private IP addresses?

    Show answer & explanation

    Correct answer: D

    The range 192.255.255.255-193.0.0.0 represents public Internet addresses, not private addresses as defined by RFC 1918. Private address ranges reserved for internal networks include 10.0.0.0/8 (Class A providing 16.7 million addresses), 172.16.0.0/12 (Class B providing 1 million addresses), and 192.168.0.0/16 (Class C providing 65,536 addresses). The specified range contains public addresses used for Internet routing and cannot be used for private networks without causing routing conflicts. Network Address Translation (NAT) is required to translate private addresses to public addresses for Internet communication, ensuring proper routing and avoiding address conflicts with global Internet addressing.

  3. Question 3

    Q3Multiple answers

    Which of the following protocols allow the root switch location to be optimized per VLAN? (Choose all that apply.)

    Show answer & explanation

    Correct answers: A, C

    Per-VLAN Spanning Tree Plus (PVST+) creates a separate spanning tree instance for each VLAN, allowing network administrators to optimize root bridge placement per VLAN for optimal traffic flow and load balancing. This Cisco proprietary enhancement enables different VLANs to use different paths through the network, preventing a single root bridge from becoming a bottleneck for all traffic. Standard STP and RSTP operate as single instances across all VLANs and cannot provide per-VLAN optimization, making them unsuitable for VLAN-specific root bridge placement in modern enterprise networks requiring load distribution and redundancy.

    Per-VLAN Rapid Spanning Tree (PVRST) combines the per-VLAN optimization of PVST+ with the rapid convergence of RSTP, creating separate spanning tree instances for each VLAN while achieving convergence in seconds rather than minutes. This allows root bridge optimization per VLAN for traffic engineering and load balancing while maintaining fast recovery from link failures. PVRST provides the best of both worlds - the flexibility of per-VLAN trees for traffic optimization and the speed of rapid convergence for network stability, making it ideal for modern enterprise networks with multiple VLANs requiring both performance and reliability.

  4. Question 4

    Q4Multiple answers

    Which two fields are present in the output of the show ip interface brief command? (Choose two.)

    Show answer & explanation

    Correct answers: C, D

    The show ip interface brief command displays the OK? field which indicates whether the interface configuration is valid and error-free. This field shows YES for properly configured interfaces or NO for interfaces with configuration issues such as invalid IP addresses, subnet mask conflicts, or duplicate address assignments. The OK? field provides immediate visibility into interface configuration health, helping network administrators quickly identify interfaces requiring attention during troubleshooting and network verification procedures.

    The Method field in show ip interface brief output indicates how the IP address was configured on each interface, displaying values like NVRAM (statically configured), DHCP (dynamically assigned), IPCP (PPP negotiated), or unset (not configured). This information helps network administrators understand the source of IP configuration for troubleshooting and documentation purposes. Other fields in the output include Interface (interface name), IP-Address (assigned IP), Status (physical status), and Protocol (data link protocol status), but YES?, Helper address, and Proxy ARP are not displayed in this specific command output.

  5. Question 5

    Q5Multiple answers

    Which two modes are Cisco Internetwork Operating System (IOS) operating modes? (Choose two.)

    Show answer & explanation

    Correct answers: B, D

    User EXEC mode is the initial command-line access level after logging into a Cisco router or switch, identified by the > prompt. This mode provides basic monitoring commands like show, ping, and telnet but restricts configuration changes for security. Users can view system status, interface statistics, and routing tables without modifying device configuration. Administrative commands requiring privileged access are blocked in User EXEC mode. The transition to privileged EXEC mode requires the enable command and potentially an enable password, providing role-based access control that prevents unauthorized configuration changes while allowing network monitoring and troubleshooting functions.

    Global configuration mode is accessed from privileged EXEC mode using the configure terminal command and is identified by the (config)# prompt. This mode enables administrators to make system-wide configuration changes affecting the entire device, including hostname, routing protocols, access control lists, and global interface parameters. Commands entered in global configuration mode are immediately active but not saved until the copy running-config startup-config command is executed. Sub-configuration modes like interface configuration, router configuration, and line configuration are accessed from global configuration mode. This hierarchical structure provides organized access to different device configuration aspects while maintaining security through privilege levels.

  6. Question 6

    Q6

    Which of the following accurately describes the purpose of a trunk?

    Show answer & explanation

    Correct answer: C

    Trunk links are designed to carry traffic for multiple VLANs simultaneously between network infrastructure devices, primarily switches. Trunking uses frame tagging protocols like IEEE 802.1Q or ISL (Inter-Switch Link) to identify which VLAN each frame belongs to as it traverses the trunk link. This enables hosts in the same VLAN but connected to different switches to communicate while maintaining VLAN isolation for security and broadcast domain separation. Trunk links are essential in multi-switch environments for extending VLANs across the network infrastructure. Without trunking, each VLAN would require a separate physical link between switches, making large VLAN deployments impractical and expensive.

  7. Question 7

    Q7

    Which Ethernet LAN contention or access method listens for a signal on the channel before transmitting data, and stops transmitting if a collision is detected?

    Show answer & explanation

    Correct answer: B

    Carrier Sense Multiple Access with Collision Detection (CSMA/CD) is the fundamental access method used in traditional Ethernet networks operating in half-duplex mode. The protocol requires devices to listen to the transmission medium before sending data (carrier sense), allows multiple devices to access the medium (multiple access), and stops transmission immediately when a collision is detected (collision detection). Upon detecting a collision, devices execute a binary exponential backoff algorithm, waiting a random time period before retransmitting. Modern full-duplex Ethernet eliminates collisions by providing separate transmit and receive paths, making CSMA/CD unnecessary in switched environments. However, understanding CSMA/CD remains crucial for troubleshooting legacy networks and hub-based segments.

  8. Question 8

    Q8Multiple answers

    What will be the effects of executing the following set of commands? (Choose all that apply.)

    router(config)# router eigrp 44

    router (config-router)# network 10.0.0.0
    router (config-router)# network 192.168.5.0

    Show answer & explanation

    Correct answers: A, C, D, E

    The router eigrp 44 command enables Enhanced Interior Gateway Routing Protocol (EIGRP) in Autonomous System (AS) 44, creating a routing process that will form adjacencies with other EIGRP routers in the same AS. The AS number is a logical identifier that must match between routers for adjacency formation and route exchange. EIGRP uses the AS number to identify routing domains and prevent inadvertent route advertisement between different administrative domains. Multiple EIGRP processes can run simultaneously on a single router using different AS numbers. The AS number also affects metric calculation and route tagging in enterprise networks with complex routing policies and redistribution requirements.

    The network 10.0.0.0 command activates EIGRP on all interfaces with IP addresses in the 10.0.0.0/8 network range, using classful network boundaries by default. Any interface matching this network statement will begin sending EIGRP hello packets, attempting to form adjacencies with neighboring EIGRP routers, and advertising connected networks. EIGRP uses wildcard masks (similar to OSPF) for precise network matching, but when omitted, it assumes classful boundaries. Interfaces activated for EIGRP will participate in the DUAL (Diffusing Update Algorithm) for loop-free routing calculations. The network statement also determines which networks are advertised to EIGRP neighbors, making it crucial for route propagation and reachability.

    The network 192.168.5.0 command enables EIGRP on interfaces within the 192.168.5.0/24 network range, activating neighbor discovery and route advertisement for this subnet. EIGRP will begin sending multicast hello packets (224.0.0.10) on matching interfaces to discover adjacent EIGRP routers. Once adjacencies form, the router will advertise this network to EIGRP neighbors and receive topology updates for optimal path calculation. The Diffusing Update Algorithm (DUAL) will calculate feasible successors and backup routes for resilient routing. Interface-specific EIGRP parameters like hello intervals, hold times, and authentication can be configured per interface for fine-tuned neighbor relationships and convergence behavior.

    Any interface with an IP address in the 10.0.5.8/16 range would be activated for EIGRP due to the network 10.0.0.0 statement, as this address falls within the Class A 10.0.0.0/8 network range. EIGRP performs classful network matching by default unless wildcard masks are specified, so the 10.0.0.0 statement encompasses all subnets within the 10.x.x.x address space. This interface would participate in EIGRP neighbor discovery, topology exchange, and route calculation processes. The DUAL algorithm would calculate metric values based on bandwidth and delay by default, with options for load and reliability inclusion. Proper subnet design and summarization become critical when activating EIGRP across large Class A networks to prevent routing table bloat.

  9. Question 9

    Q9

    Users on the LAN are unable to access the Internet. How would you correct the immediate problem?

    Router# show ip interface brief
    Interface IP-Address OK? Method Status
    Protocol FastEthernet 0/0 unassigned YES
    unset down down FastEthernet 0/1
    172.16.1.254 YES NVRAM up up
    Serial0/0 200.16.4.25 YES NVRAM administratively down
    down Serial0/1 unassigned YES
    unset down down

    Question 9 image
    Show answer & explanation

    Correct answer: B

    Explanation:

    The output indicates that the serial interface leading to the Internet is administratively down. All router interfaces are disabled by default due to the presence of a shutdown command in the running configuration. The no shutdown command removes this configuration, and the interface becomes active. The command sequence is:

    Router(config)# interface serial0/0 Router(config-if)# no shutdown

    Although it was not the problem in the scenario, the S0/0 interface could also cause an error if it is configured as shown in this output:

    Interface IP-Address OK? Method Status Protocol Serial0/0 200.16.4.25 YES NVRAM up down
    In this example, the S0/0 interface has been enabled, and while there is Layer 1 connectivity (the Status column), Layer 2 is not functioning (the Protocol column). There are two possible reasons for this result:

    Configuring a bandwidth on the serial interface is incorrect because the output indicates the interface is administratively down, which does not pertain to bandwidth.

    Configuring a private IP address on the Fastethernet0/0 LAN interface is incorrect because the output indicates the problem is with the disabled serial interface.

    The IP address on the serial interface may or may not be valid, but it is not the immediate cause of the connectivity problem. The serial interface is disabled.

    Objective:

    LAN Switching Fundamentals Sub-Objective:
    Troubleshoot interface and cable issues (collisions, errors, duplex, speed)

    References:

    Cisco > Support > Administrative Commands > shutdown

  10. Question 10

    Q10

    When a packet is forwarded through a network from one host to another host, which of the following fields in the Ethernet frame will change at every hop?

    Show answer & explanation

    Correct answer: B

    When packets traverse routers between different network segments, the destination MAC address changes at each hop to reflect the next-hop MAC address required for Layer 2 forwarding. Initially, the destination MAC is the local router default gateway MAC, then it becomes the next-hop router MAC for inter-router communication, and finally the destination host MAC on the target segment. This MAC address rewriting is essential for proper frame delivery as MAC addresses only have significance within individual collision domains. Routers strip and rebuild Ethernet headers for each network segment while preserving Layer 3 IP addresses throughout the routing process. Understanding MAC address changes during routing is fundamental to troubleshooting connectivity issues across routed networks.

  11. Question 11

    Q11

    Which Cisco IOS Cisco Discovery Protocol (CDP) command displays the IP address of the directly connected Cisco devices?

    Show answer & explanation

    Correct answer: D

    References:

    Cisco > Cisco IOS Network Management Command Reference > schema through show event manager session cli username > show cdp neighbors detail

Register free to unlock 12 more sample questions

Create a free account to continue with the rest of the 200-301 sample set.

Lifetime One

Own this practice test forever.

$79.99
$75.99
one-time
  • Full access to 875 questions
  • Study, Timed & Flashcard Modes
  • All past and future versions i
  • Detailed Explanations
  • Study Tracking & Past Attempts
  • Brainy AI Assistant
  • Lifetime updates

Two

Any 2 exams per month.

$20.00/exam
$39.99
/month
  • 2 active exam slots
  • Study, Timed & Flashcard Modes
  • All past and future versions i
  • Detailed Explanations
  • Study Tracking & Past Attempts
  • 1,000 Brainy AI Credits
  • Cancel anytime

Premium Twelve

Any 12 exams over 3 months.

$15.00/exam
$179.99
/3 months
  • 4 active exam slots
  • Study, Timed & Flashcard Modes
  • All past and future versions i
  • Detailed Explanations
  • Study Tracking & Past Attempts
  • 15,000 Brainy AI Credits
  • Dedicated support
  • Friend seat included — full access

Trusted by professionals at

NvidiaSupabaseGitHubOpenAITursoClerkClaude AIAmazon